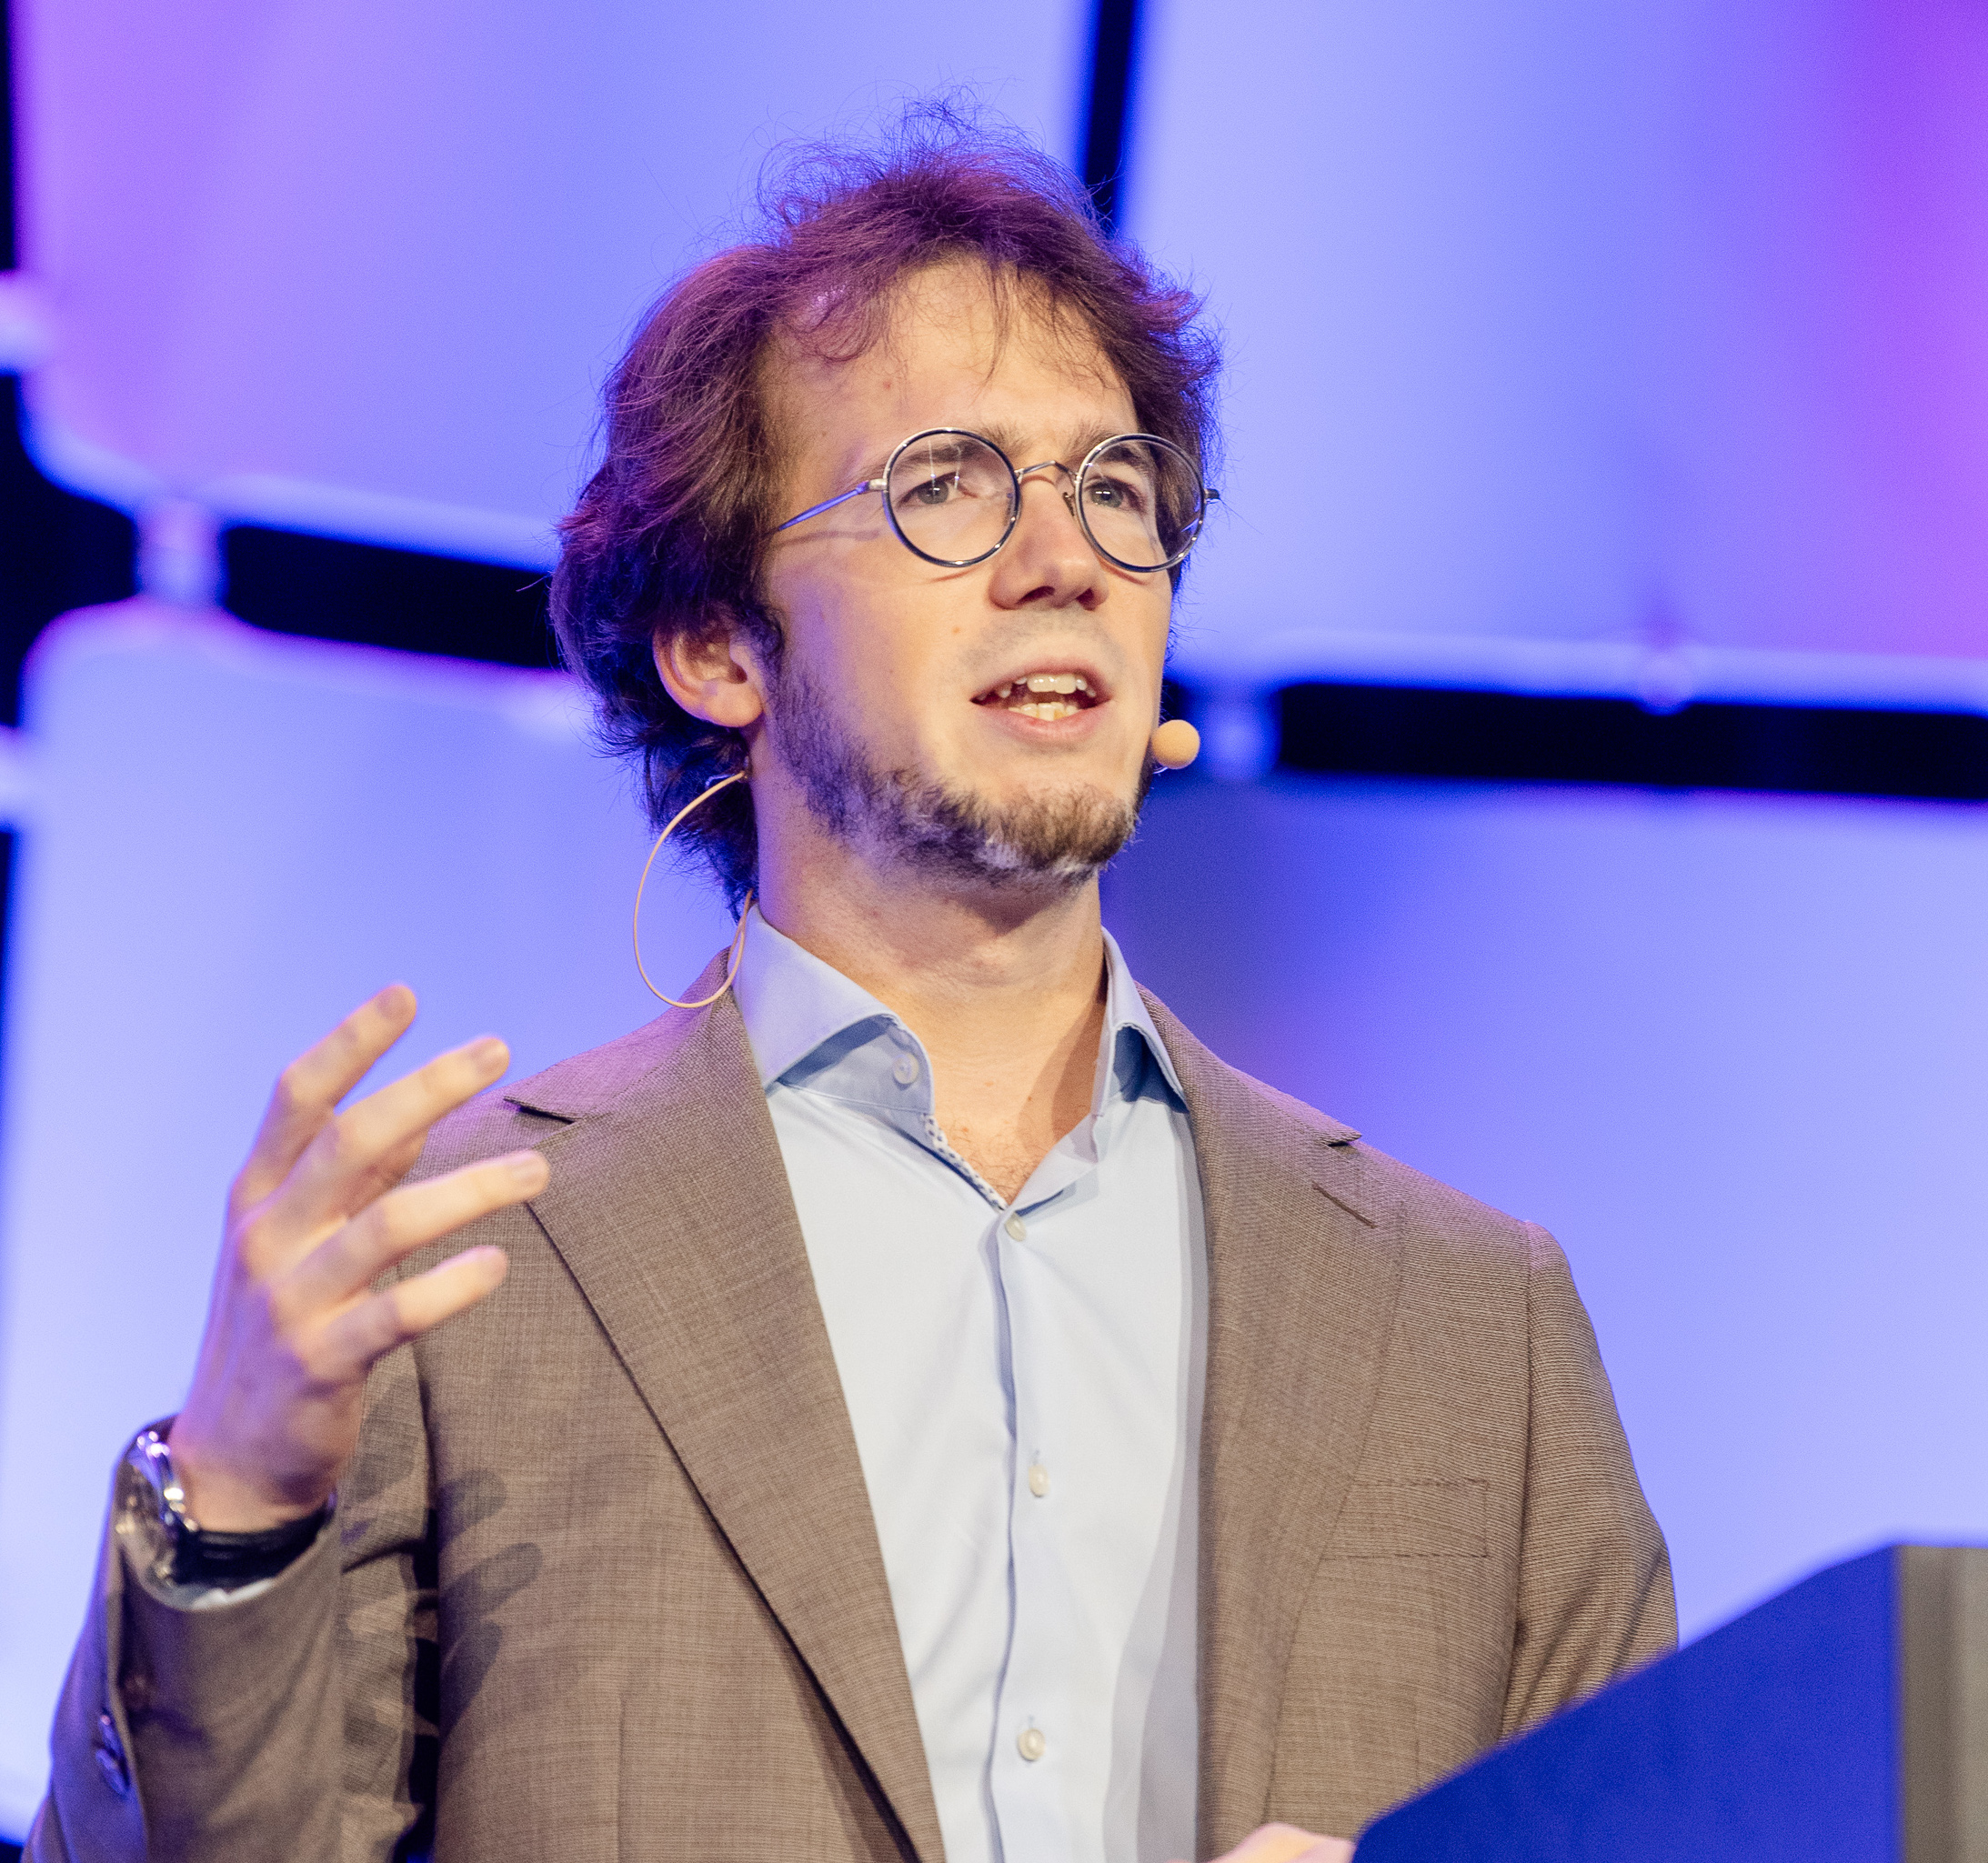
Yolan Romailler
Head of Security
Bio
Yolan is an applied cryptographer delving into (and dwelling on) cryptography, secure coding, and other fun things. He has previously spoken at Black Hat USA, NorthSec, GopherCon, Real World Crypto and DEF CON on topics including automation in cryptography, public keys vulnerabilities, elliptic curves, post-quantum cryptography, functional encryption, open source security, distributed randomness, and more! He notably introduced the first practical fault attack against the EdDSA signature scheme.
Lately he's been working on threshold cryptography, including VRFs, distributed key generation, and timelock encryption. He was one of the co-founders of Randamu, whose mission was to push threshold cryptography forward and nowadays he works on securing AI from weights to inference, using Trusted Execution Environment and thoughtful designs.

You are viewing Yolan Romailler's limited profile. Login to access details such as social profiles, projects & office hours.
Contact Details
Contributions (4)
 Attendee
LabWeek Web 3
Nov 2025
LabWeek Web 3
Nov 2025
Berlin Blockchain Week 2025
Jun 2025
Berlin Blockchain Week 2025
Jun 2025
LabWeek Web3
Nov 2024
LabWeek Web3
Nov 2024
EthCC
Jul 2024
EthCC
Jul 2024